SFTP file transfer reference
SSH is the transport mechanism. SFTP is a file transfer protocol. PGP is used to provide encryption of data.
The intended audience for this document is:
- Developers who need to generate SSH and PGP key pairs to establish secure SFTP connectivity with Westpac.
- Developers who need to automate file encryption, decryption, and file transfer processes.
Overview
Secure Shell (SSH) is a widely-used Transport Layer protocol for secure communications over an insecure network.
SSH provides strong symmetric-key encryption, asymmetric-key host authentication, and data integrity protection.
Westpac provides an SSH server that is restricted to file transfer operations, enabling customers to securely upload files to Westpac or retrieve files from Westpac.
Westpac's SSH server is primarily intended for batch processing. For real-time integration requirements, please consider our REST file transfer API solution.
This page details the configuration of SSH and PGP, enabling customers to securely exchange files with Westpac.
Transfer protocols
Secure Shell (SSH)
SSH is the transport mechanism used to securely deliver files.
It is an encrypted protocol that provides secure communication between two systems. The file transfer protocol used over SSH is typically either SCP (Secure Copy Protocol) or SFTP (SSH File Transfer Protocol).
Secure Copy Protocol (SCP)
SCP (Secure Copy Protocol) is a file transfer protocol used to copy files between two hosts over SSH. It is typically used for non-interactive file transfers and can transfer one or more files in a single operation.
You can think of SCP as being similar to a standard file copy operation, but performed securely between systems over a network.
SSH File Transfer Protocol (SFTP)
SFTP (SSH File Transfer Protocol) is a full-featured file management protocol. In addition to transferring files, it supports operations such as browsing remote directories, listing files, creating and removing directories, and renaming files.
You can think of SFTP as the secure equivalent of a traditional interactive FTP session.
A wide range of SSH clients are available, including both free and commercial products. The choice of SSH client is at the customer's discretion, provided it supports the cryptographic algorithms required by Westpac. Westpac recommends the following interactive SSH clients:
- Your operating system's built-in OpenSSH client
- WinSCP
Security
As is standard with SSH, only your SSH public key is required to establish a connection to Westpac's SSH server.
All files transferred between Westpac and customer systems must also be encrypted and digitally signed using PGP, in accordance with Westpac's security policy.
This provides two key security benefits:
- Confidentiality - Files remain encrypted while at rest, ensuring that their contents cannot be accessed by unauthorised parties.
- Non-repudiation - Digital signatures created using public/private key pairs allow both Westpac and the customer to verify that a file originated from a trusted source and has not been altered in transit or since it was signed.
Westpac recommends the following products for file encryption and digital signing:
Delivery assurance
SSH does not provide an application-level delivery guarantee. However, the file transfer and processing workflows implemented by both Westpac and the customer can be used to verify that files have been successfully transferred and processed.
File transfers with Westpac generally fall into one of two scenarios:
Pushing files to Westpac
After a customer transfers a file to Westpac, the file is automatically collected and processed by Westpac's file processing platform.
As part of the PGP decryption and signature verification process, integrity checks are performed on the file. If the file has been corrupted, modified, or cannot be successfully decrypted, processing will fail and a notification email will be sent to the customer.
Polling files from Westpac
When a customer retrieves and decrypts a file from Westpac, the same PGP integrity and signature verification checks are performed. If the file has been corrupted or altered, decryption or signature verification will fail, indicating that the file cannot be trusted.
Customers are responsible for ensuring that their file retrieval processes and scheduled tasks are operating correctly. As Westpac does not control customer systems, it cannot guarantee that file polling has occurred or that files have been successfully retrieved.
Quick Start
- The Qvalent Implementation Consultant creates an iLink Test account for the customer's technical contact.
- The customer contact completes the iLink Connectivity Form in the Test environment.
- The Qvalent Implementation Consultant arranges configuration of the Test SFTP server.
- The customer configures their SFTP software and/or automation.
- The customer performs testing in the Test environment.
- Once testing is complete and the customer is satisfied with the results, a sign-off email must be provided before progressing to production.
- The Qvalent Implementation Consultant creates an iLink Production account for the customer's technical contact.
- The customer contact completes the iLink Connectivity Form in the Production environment.
- The Qvalent Implementation Consultant arranges configuration of the Production SFTP server.
- The customer tests the SFTP connection in the Production environment.
- Once connectivity testing has been successfully completed, the customer may perform low-value live testing of any other Westpac products being implemented.
Transfer overview
- Initial key exchange.
- Pushing a file to Westpac.
- Polling a file from Westpac.
- Receiving files from Westpac.
- File and directory names.
- Network connectivity.
- Environments.
Initial key exchange
Push / Poll
This integration model is intended for customers who upload files to Westpac and retrieve files from Westpac using SFTP.
To establish the SSH connection and exchange files securely, two public keys must be provided to Westpac:
- Your SSH public key - Used to authenticate the customer's SSH client when establishing a connection to Westpac's SFTP server.
- Your PGP public key - Used by Westpac to encrypt files sent to the customer and to verify digital signatures applied by the customer.
These keys must be uploaded through the iLink Connectivity Setup screens.
In return, Westpac will provide:
- Our SSH host key - Used by the customer to verify the identity of the server when establishing a SSH connection.
- Our PGP public key - Used by the customer to encrypt files sent to Westpac and to verify digital signatures applied by Westpac.
Push / Push
This integration model is intended for customers who upload files to Westpac and receive files from Westpac via an SFTP server hosted within their environment.
To establish the SSH connection and exchange files securely, three public keys must be provided to Westpac:
- Your SSH public key - Used to authenticate the customer's SSH client when establishing a connection to Westpac's SFTP server.
- Your SSH host key - Used by Westpac to verify the identity of the customer's SSH server when establishing an outbound SSH connection.
- Your PGP public key - Used by Westpac to encrypt files sent to the customer and to verify digital signatures applied by the customer.
These keys must be uploaded through the iLink Connectivity Setup screens.
In return, Westpac will provide:
- Our SSH public key - Used to authenticate the SSH client that Westpac uses when establishing a connection to the customer's SSH server.
- Our SSH host key - Used by the customer to verify the identity of the server when establishing a SSH connection.
- Our PGP public key - Used by the customer to encrypt files sent to Westpac and to verify digital signatures applied by Westpac.
Pushing a file to Westpac
To push a file to Westpac:
- Encrypt the file using Westpac's PGP public key and digitally sign it using the customer's PGP private key. Files must be ASCII-armoured and compressed before transmission.
- Transfer the file using an SSH client configured with the connection details provided by Westpac. During connection establishment, Westpac authenticates the customer using the SSH public key exchanged during the Initial key exchange.
- Once the SSH connection has been established, the file is transferred to Westpac's SFTP server.
- Westpac's file processing platform detects the uploaded file and retrieves it for processing. The digital signature is verified using the customer's PGP public key. If signature verification is successful, the file is decrypted using Westpac's PGP private key.
Once the digital signature has been verified and the file has been successfully decrypted, the file is processed.
Polling a file from Westpac
To poll a file from Westpac:
- Westpac encrypts the file using the customer's PGP public key, digitally signs it using Westpac's PGP private key, and ASCII-armours the resulting file. The file is then placed in a pickup directory.
- The customer's SSH client connects to Westpac's SFTP server using the SSH key configured during the Initial key exchange.
- Once connected, the customer retrieves the file using SFTP. File retrieval should be performed according to the agreed file naming conventions.
- After the file has been downloaded, the customer verifies the digital signature using Westpac's PGP public key and decrypts the file using the customer's PGP private key.
Once the digital signature has been verified and the file has been successfully decrypted, the file can be processed.
Westpac retains files on its SFTP server for 30 days. Files that have not been retrieved within this period are automatically deleted.
Receiving files from Westpac
Some customers choose to implement a push-push SFTP model, where Westpac delivers files directly to an SFTP server hosted within the customer's environment.
- Westpac encrypts the file using the customer's PGP public key, digitally signs it using Westpac's PGP private key, and ASCII-armours the resulting file. The file is then transferred to the customer's SFTP server.
- Once the customer has received the file, they should verify the digital signature using Westpac's PGP public key. If signature verification is successful, the file can be decrypted using the customer's PGP private key.
Once the digital signature has been verified and the file has been successfully decrypted, the file can be processed.
File and directory names
File names may follow any naming convention, provided they contain only valid ASCII characters and are valid for the target operating system and SFTP server.
Westpac recommends the following:
- Include a date or timestamp in the file name.
- Avoid using spaces in file names, as they can complicate command-line scripting and automation.
Destination directories and file naming conventions are agreed between the customer and Westpac during implementation. Where no customer-specific convention has been defined, default file names are typically used in accordance with the recommendations above.
Network connectivity
As part of the iLink connectivity setup, you must provide the public source IP address of the system that will establish SSH connections to Westpac. Any network address translation (NAT), firewalls, or proxy devices should also be taken into consideration.
Westpac will update its firewall configuration to permit connections from your nominated source IP address to Westpac's SSH server on TCP port 22.
You may also need to engage your network administrators to ensure that outbound SSH connections on TCP port 22 are permitted from your environment.
Environments
| Environment | Connection Details |
|---|---|
| Test | Configure your SSH client to connect to ssiw.support.qvalent.com (203.39.159.31) on TCP port 22. |
| Production | Configure your SSH client to connect to ssiw.qvalent.com (192.170.86.151) on TCP port 22. |
iLink connectivity setup
During the early stages of your Westpac implementation project, you will be asked to nominate a technical contact who will be responsible for establishing connectivity.
Once these details have been provided, the technical contact will receive access to the iLink portal, where your organisation's network connectivity information can be submitted.
The iLink connectivity process consists of the following steps:
- The Qvalent Implementation Consultant provides the technical contact with access to the iLink Test environment.
- Complete and submit the setup connectivity form.
- Notify your Qvalent and Westpac implementation managers that the form has been submitted.
- The Qvalent Implementation Consultant configures the required file routing and notifies stakeholders once the configuration is complete.
- Exchange test files with Westpac to validate connectivity and file routing.
- Once testing has been successfully completed and approved, steps 1–5 are repeated for the Production environment.
iLink URLs
| Environment | URL |
|---|---|
| Test | https://ilink.support.qvalent.com/ |
| Production | https://ilink.westpac.com.au/ |
Setup connectivity form
To configure connectivity, select Connectivity from the navigation menu and then click Setup connectivity.
The Setup connectivity page will be displayed, allowing you to provide the following information:
- Contact emails - Additional email addresses that should receive connectivity-related notifications.
- Your PGP public key - Files exchanged via SFTP are encrypted using PGP. Your PGP public key is required so that files sent by Westpac can be encrypted and decrypted by your systems.
- Your PGP signing key (optional) - If you use a dedicated PGP key pair for digital signatures, provide the public signing key here. If no signing key is supplied, your PGP public key will be used for both encryption and signature verification.
- Your SSH public key - Westpac's SFTP service uses SSH public key authentication rather than passwords. Your SSH public key is required to authenticate connections.
- Your source IP address(es) - Access to the service is restricted to approved source IP addresses. Provide the public IP address or CIDR range from which your SFTP connections will originate. Ensure these are your externally visible IP addresses after any NAT, proxy, firewall, or other network infrastructure has been taken into account. You can determine the IP address seen by Westpac by logging in to iLink and viewing the address displayed in the IP Addresses section of the connectivity form.
For customers who require Westpac to deliver files to their SFTP server, the following additional information must be provided:
- Your SFTP server details - This section contains the connection details that Westpac will use when establishing an SFTP session to your server and placing files for collection. The account provided must have sufficient permissions to write files to the nominated directory.
- Your SSH host key - Westpac uses your server's SSH host key to verify the identity of the server before establishing a connection. This key is typically provided as a long string of encoded text. If your SFTP service is hosted behind a load balancer and multiple backend servers present different host keys, you may provide an alternate host key to allow successful validation regardless of which server handles the connection.
Getting Westpac's server details
After you submit the Connectivity form, it will be reviewed and processed, typically within 3–5 business days. Once the setup has been completed, you will receive an email notification advising that connectivity testing can begin.
Users with access to the iLink Connectivity Setup page will then be able to view the following information:
- Westpac's PGP public key - This public key is used to encrypt files sent to Westpac. It should also be used to verify digital signatures applied by Westpac to files that you receive.
- Westpac's SSH host key - This is the public SSH host key presented by Westpac's SFTP server. It should be validated and trusted by your SFTP client to verify the identity of the server when establishing a connection.
- Westpac's SFTP server details - This section contains the connection details required to access Westpac's SFTP service, including your assigned username and the directories used for uploading files to Westpac (incoming) and retrieving files from Westpac (outgoing).
- Your uploaded keys - These fields allow you to verify which SSH and PGP keys have been configured in iLink.
Software recommendations
To connect to Westpac's SFTP service and perform PGP encryption and decryption, you will require an SSH client and PGP software.
Westpac recommends the following software products; however, customers may choose any equivalent software that meets the technical and security requirements of the solution.
SSH client software
| SSH client | Description |
|---|---|
| OpenSSH | OpenSSH is the de facto SSH client implementation and is commonly installed by default on Unix and Linux systems. OpenSSH is also available as an optional feature on Windows. |
| WinSCP | WinSCP is a widely used graphical SFTP and SCP client for Windows. For most environments, WinSCP can be installed using the default installation options. |
Supported SSH algorithms
Your SSH client must support at least one of each of the following algorithms for each type:
| Algorithm Type | Supported Algorithms |
|---|---|
| Key exchange algorithms | diffie-hellman-gex-sha256 diffie-hellman-group14-sha256 diffie-hellman-group15-sha512 diffie-hellman-group16-sha512 ecdh-sha2-nistp256 ecdh-sha2-nistp384 ecdh-sha2-nistp521 curve25519-sha256 curve25519-sha256@libssh.org |
| Server host key algorithms | rsa-sha2-256 rsa-sha2-512 |
| Encryption algorithms | aes128-ctr aes192-ctr aes256-ctr aes128-gcm@openssh.com aes256-gcm@openssh.com |
| Mac algorithms | hmac-sha2-256 |
| Compression algorithms | zlib none |
PGP software
| PGP software | Description |
|---|---|
| GnuPG / Gpg4win | GnuPG is a widely used open-source OpenPGP implementation and is commonly installed by default on Unix and Linux systems. GnuPG is also available on Windows through the Gpg4win distribution. |
| SDS E-Business Server | SDS E-Business Server is an enterprise-supported OpenPGP solution available on Unix, Linux and Windows systems. |
SSH key generation
Westpac's SSH server supports the following SSH public key types:
- RSA 2048-bit and 4096-bit
- ECDSA P-256, P-384, and P-521
- Ed25519
Westpac recommends Ed25519 for new implementations. Ed25519 is a modern elliptic-curve algorithm that provides strong security, smaller key sizes, and faster cryptographic operations than RSA, while maintaining broad support across current SSH clients and servers.
Generating a SSH key with ssh-keygen (OpenSSH)
To generate an Ed25519 SSH key pair with ssh-keygen:
$ ssh-keygen -t ed25519 -C "<Company Name> SSH Key"Replace <Company Name> with your company name. The comment is used to help identify the owner of the key.
This command generates an Ed25519 public/private key pair. During key generation, you will be prompted to enter a passphrase to protect the private key. While using a passphrase is recommended for security, it may prevent fully unattended SFTP or SCP transfers unless an SSH agent or equivalent key management solution is used to supply the passphrase automatically.
The output will be similar to the following:
$ ssh-keygen -t ed25519 -C "Example SSH Key"
Generating public/private ed25519 key pair.
Enter file in which to save the key (/home/exampleuser/.ssh/id_ed25519):
Created directory '/home/exampleuser/.ssh'.
Enter passphrase for "/home/exampleuser/.ssh/id_ed25519" (empty for no passphrase):
Enter same passphrase again:
Your identification has been saved in /home/exampleuser/.ssh/id_ed25519
Your public key has been saved in /home/exampleuser/.ssh/id_ed25519.pub
The key fingerprint is:
SHA256:FFLD74R+hfKPYNdjRwcezap6oRa/IBrXl4Jbsfjtpsg Example SSH Key
The key's randomart image is:
+--[ED25519 256]--+
|      .o+      o |
|       ..o    o o|
|        .o . . + |
|       .o + . + .|
|       .S=.o o . |
|        ++*o*..  |
|      ..=+*Oo+   |
|       = *===    |
|      . E.o=+.   |
+----[SHA256]-----+
If you accept the default file locations, the generated keys will be stored in the ~/.ssh directory. The private key will be named id_ed25519 and the public key will be named id_ed25519.pub.
Provide the contents of id_ed25519.pub to Westpac through the iLink Connectivity Setup screens. Never share the private key (id_ed25519), as it is used to authenticate your identity and must remain confidential.
The SSH public key will be similar to the following:
$ cd ~/.ssh
$ more id_ed25519.pub
ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIOloIslAUWnxKmF9Azhkkeak14viAf+F8xFnfKvTFXq7 Example SSH Key
Generating a SSH key with PuTTYgen (WinSCP)
To generate an Ed25519 SSH key pair with PuTTYgen:
Step 1: Launch PuTTYgen, which is included with WinSCP. PuTTYgen can be opened from the WinSCP Login dialog by selecting Tools -> Run PuTTYgen.
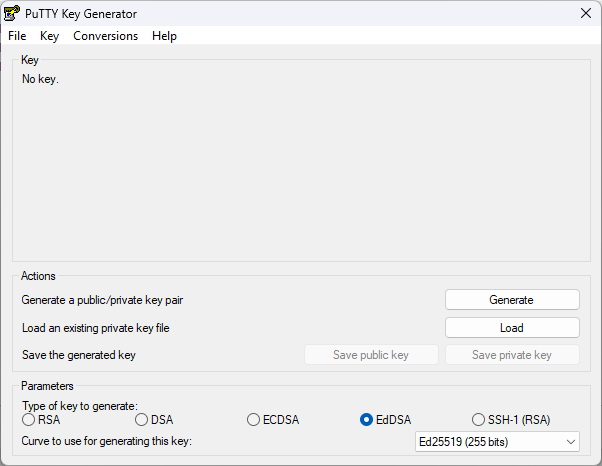
Step 2: Under Parameters, select EdDSA as the key type and ensure Ed25519 (255 bits) is selected as the curve. Click Generate.
Follow the on-screen instructions and move the mouse pointer within the PuTTYgen window to provide entropy for key generation.
Update the Key comment field to "<Company Name> SSH Key", replacing <Company Name> with your company name. The comment is used to help identify the owner of the key.
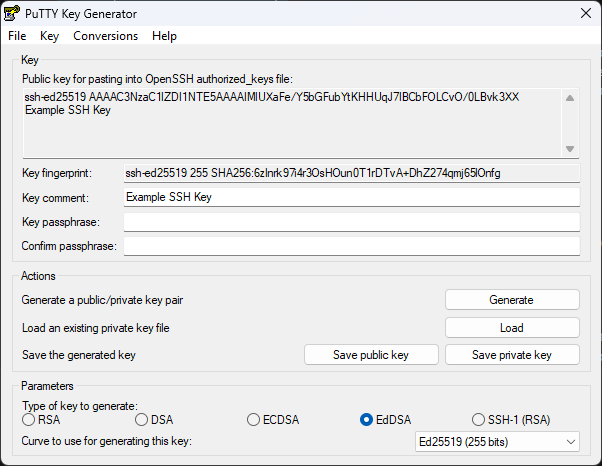
Click Save public key and save the key to a file named <YourCompanyName>_ssh_key.pub, replacing <YourCompanyName> with your company name without spaces.
This file contains your SSH public key and must be provided to Westpac as part of the iLink Connectivity Setup process.
Step 3: While PuTTYgen is still open, click Save private key and acknowledge the passphrase warning. While using a passphrase is recommended for security, it may prevent fully unattended SFTP or SCP transfers unless an SSH agent or equivalent key management solution is used to supply the passphrase automatically.
Save the private key to a secure location. This file contains your SSH private key and must never be shared, as it is used to authenticate your identity and must remain confidential.
Testing the SSH connection
Before testing connectivity between your SSH client and Westpac's SFTP service, confirm the following:
- You have provided your server's public IP address and Westpac has confirmed that the address has been allowed through its firewall on TCP port 22.
- Your network firewalls permit outbound connections to Westpac's SFTP service on TCP port 22.
- You have provided your SSH public key and PGP public key to Westpac.
- Westpac has provided you with their PGP public key.
- Westpac has provided your assigned SFTP username, and you have generated an SSH key pair.
Once these prerequisites have been met, you can proceed with testing the SSH connection.
Testing basic connectivity (TCP)
Before testing SSH authentication, confirm that basic TCP connectivity to Westpac's SFTP service is working.
Unix and Linux
Run the following command to use netcat to establish a TCP connection, replacing <host> with the appropriate host name from the Environments section.
If netcat is not installed, install it from your operating system's package repository before continuing.
$ nc -vz <host> 22If connectivity is successful, output similar to the following will be displayed:
Ncat: Connected to 203.39.159.31:22.
Ncat: 0 bytes sent, 0 bytes received in 0.01 seconds.
A successful connection confirms that your server can establish a TCP connection to the remote server on port 22.
If the connection fails, verify that the host name is correct, confirm that outbound connections on port 22 are permitted by your network and firewall policies, and consult your network administrator if the issue persists.
Windows
Open a PowerShell window and run the following command, replacing <host> with the appropriate host name from the Environments section:
PS> Test-NetConnection <host> -Port 22If connectivity is successful, output similar to the following will be displayed:
ComputerName     : ssiw.support.qvalent.com
RemoteAddress    : 203.39.159.31
RemotePort       : 22
InterfaceAlias   : Ethernet
SourceAddress    : 192.168.1.1
TcpTestSucceeded : True
A value of True for TcpTestSucceeded confirms that a TCP connection to the remote server on port 22 was successfully established.
A value of False for TcpTestSucceeded indicates that a connection could not be established. Consult your network administrator to verify connectivity, routing, firewall rules, and any required IP address allow-listing.
Testing SSH connectivity
Once basic TCP connectivity has been confirmed, you can test SSH authentication and establish an SFTP session.
OpenSSH
Run the following command to connect to Westpac's SFTP service. Use the -i option to specify the private key to use for authentication. If no private key is specified, OpenSSH will use its default key locations (for example, ~/.ssh/id_ed25519).
Replace <username> with your assigned SFTP username and <host> with the appropriate host name from the Environments section.
$ sftp -i <privatekey> <username>@<host>On the first connection, you will be prompted to verify and trust Westpac's SSH host key. Confirm that the displayed fingerprint matches the SSH host key fingerprint provided on the iLink Connectivity Setup screen, then type yes to continue. If the fingerprint does not match the value provided by Westpac, do not continue with the connection and contact your Qvalent Implementation Consultant.
If connectivity is successful, output similar to the following will be displayed:
The authenticity of host 'ssiw.support.qvalent.com (203.39.159.31)' can't be established.
RSA key fingerprint is SHA256:KjxPV15ymns/rUEiOCFaZB2EmFt/FHdnNZ0zWbrsvc8.
This key is not known by any other names.
Are you sure you want to continue connecting (yes/no/[fingerprint])? yes
Warning: Permanently added 'ssiw.support.qvalent.com' (RSA) to the list of known hosts.
Connected to ssiw.support.qvalent.com.
sftp>
If the connection is closed immediately after authentication and you receive a Connection closed. error, refer to the Troubleshooting section for further guidance.
WinSCP
Step 1: Launch WinSCP and create a new site. Enter the Host name and User name provided by Westpac.
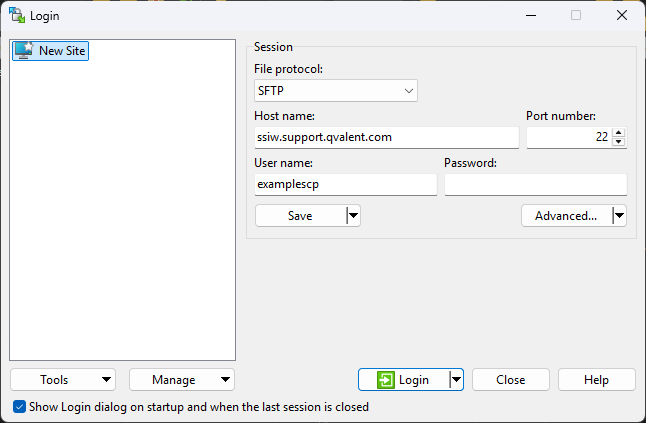
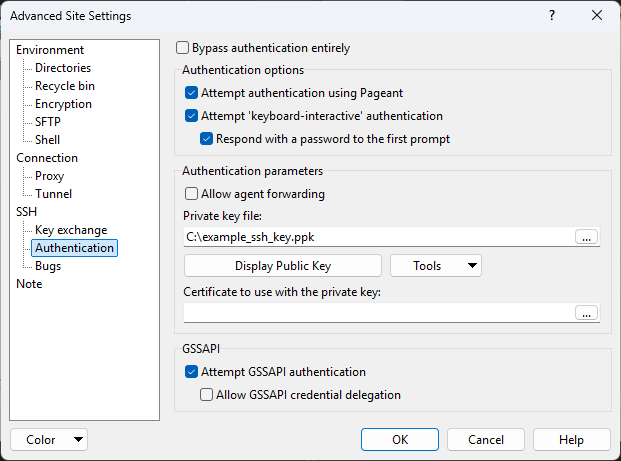
Step 2: To authenticate using your SSH key, click Advanced.... In the left-hand navigation pane, select SSH -> Authentication, then select the .ppk private key file generated previously using PuTTYgen and click OK.
Step 3: Click Save to save the configuration as a new site. Then click Login to connect to Westpac's SFTP service. If this is your first connection, you may be prompted to verify and trust Westpac's SSH host key before the connection is established.
A successful connection will display the files and directories available on Westpac's SFTP service in the right-hand pane.
PGP key generation
Generating a PGP key pair with GnuPG
You must generate a PGP key pair consisting of a public key and a private key. The public key is provided to the organisations you exchange files with, while the private key must be kept secure and never shared.
Your keyring will contain your own key pair and the public keys of any business partners (such as Westpac). Public keys are used to encrypt files and verify digital signatures, while private keys are used to decrypt files and create digital signatures.
The following commands apply to both Unix/Linux and Windows versions of GnuPG.
Configure loopback PIN entry mode (optional)
If GnuPG is being used on a headless server or in an automated environment, you may need to configure loopback PIN entry mode. Add the following line to ~/.gnupg/gpg.conf (or %APPDATA%\gnupg\gpg.conf on Windows):
pinentry-mode loopbackThis setting allows GnuPG to request passphrases directly from the command line or calling application instead of launching an interactive pinentry program.
Create a PGP key pair
$ gpg --full-gen-keyChoose RSA and RSA, then select your preferred key length and optional key expiry period.
If you set an expiry period, the key will no longer be accepted after the expiry date. It is your responsibility to generate a new key pair and upload the new public key through the iLink Connectivity Setup process before the existing key expires, to avoid any interruption to file transfers.
You will next be prompted to enter a Real name and Email address to create the PGP user ID, enter your company name and company contact email.
You will then be prompted to create a passphrase to protect the private key. While the use of a passphrase is recommended, it may require additional configuration in automated environments where files are encrypted, decrypted, or signed without user interaction.
By default, GnuPG stores its keyring and configuration files in the ~/.gnupg/ directory (or %APPDATA%\gnupg\ on Windows). To use an alternative location, specify the --homedir parameter when running GnuPG commands. Ensure that the files in this directory are included in your backup procedures and are not accidentally deleted. Loss of a private key may prevent you from decrypting previously encrypted files or creating digital signatures.
Exporting your PGP public key with GnuPG
Once your PGP key pair has been generated, you must export your public key and provide it to Westpac.
List your installed keys
$ gpg --list-keysReview the output and identify the key ID or email address associated with the key you wish to export.
Export your PGP public key to an ASCII-armoured file
$ gpg --armor --output <company-name>.pub --export <key-id>Replace:
<company-name>with your company name.<key-id>with the key ID, fingerprint, or email address of the key to export.
The output of these commands will be similar to the following:
$ gpg --list-keys
[keyboxd]
---------
pub   rsa2048 2026-07-20 [SC]
      1CCA7D839880E7436BD78B929922BEC6509E9413
uid           [ultimate] Example (Example key pair) <example@example.com>
sub   rsa2048 2026-07-20 [E]

$ gpg --armor --output example.pub --export example@example.com
$ more example.pub
-----BEGIN PGP PUBLIC KEY BLOCK-----

mQENBGpdwwoBCADLqLU9c78Do4ecaxqjh+2H7Vlvw/jZ+TasFEbnahQcTabsc82x
NbknfyH/oLsFqvrD9V4WvWkKY48+2/lIqI5+wexxAF2/UO7IYRGwJf3jX38wwiC4
icCQO7YTGTBmyNaB2V/vzX+5XyBM6i/xc5mNm3G1Sz45kmbZZ2qcj2KrfiXGIvAC
k9A20cKli3jZKarDYGgJjuV8T/FnEYyP8r5gqw800jeg/y6Fwb3HzYNg4tF3CGt6
W7AjHJMWExIwabCOmjc09gpgttf6HA74ZQdIzJzxB/ufoKuNllsunN8asWOjRQtM
RZEKJdUUeplxNCQ68HoJFSIABkV6xDx2EG+RABEBAAG0MEV4YW1wbGUgKEV4YW1w
bGUga2V5IHBhaXIpIDxleGFtcGxlQGV4YW1wbGUuY29tPokBUQQTAQgAOxYhBBzK
fYOYgOdDa9eLkpkivsZQnpQTBQJqXcMKAhsDBQsJCAcCAiICBhUKCQgLAgQWAgMB
Ah4HAheAAAoJEJkivsZQnpQTAKQH/2qUOTtIgNRLipZ04aO2HLuPgHSEHSEavGtK
rRuNgEf4O9jeXxkr/uqACVKk5BXxBMLKAN9Xuob8wlnoC+62VArHlr7jE/PVfkR7
VnhKXE7cXmKjOh7kASZWi856elK2e0ORSglQM/eNo/ZNEZRmdXsxE2p5viQfEUXL
Op3pjX7O5d+/Qck5GiSRxrpmdefBEWKoqTpQl7VHhTnoZTHcsf8Uu4C18K7LHET+
bres2ZNiIJVlArCeKvbb5lsNXbCQV5DavoZYoijtFCmtL4fXEM6XONJs85LA/lZk
F5m5tS2QbqlovC9CCftqa5xsdJGIxoyQgOF1RbxeRar1RCohWAC5AQ0Eal3DCgEI
AMGJlHhfm1yue0rkS2amabAJ8xkB0yw6fAvG2DkZYIcE6u5SsASK/t3ng1UB0Uuw
soogyMhqoKiPQlpzMWl3ws7YbaIulLHvRwzxUFrJaRxnmSO6Ch+dzsZaGkhZNbGr
KRBOO3oYJNtwbWAERQtH8QD7/KJl/RMIoMAaAlMVMwsPYdhbR26srCpbt4kZjM+D
qXtcwrA9oF4aWuaMDSG434DKQBuDwApPdrJMugnITTIzpgrR2Jr4v9d2jVQ+c/J4
QsI2/5QY7f8/YoBs1UB0915EOK6l1CaZJYqIocm+XpQ1tHcEJoh90OKP/UEcaRno
sw67pPEtKu+YpG4LA+dqOHUAEQEAAYkBNgQYAQgAIBYhBBzKfYOYgOdDa9eLkpki
vsZQnpQTBQJqXcMKAhsMAAoJEJkivsZQnpQTjUUIAJzZ4i7jL+/D3ABHk/z6KbkE
RfNkDfIhKjwQ08+TK0tks9W0yMqUQTiBIIMhnH8tdZhmsu084aMVYYxVpr0PNaNW
5g8pxAeDLff8iv38rwc/Ww+Pyb2DKZqAEpqlCVWpIcJPDMy94EBqFVJimyK/QefG
vx5a2Yyz/d3QRQQrQ8aolKl5tJvy5gAKN0LW8UTtBAz2AfDFWNc2R8bJU2AGy0A4
BRrLJShh/XReX3DtMnzECgw6KIIuT/17MrGRitDLHMqux1Q7vyrzGSn1ZViBBBMv
9utgjPBtGIyB1Hb8IwaWHsADD3d/XIhMXPk1GnPqYHvnBQlALzMDRfoxWXHtp1w=
=Ik+4
-----END PGP PUBLIC KEY BLOCK-----
The exported file contains your ASCII-armoured PGP public key. Provide this file to Westpac through the iLink Connectivity Setup process.
Do not provide your private key. The private key is used to decrypt files and create digital signatures, and must remain confidential.
Check the fingerprint of your PGP public key
$ gpg --keyid-format=0xshort --fingerprint <key-id>Replace <key-id> with the key ID, fingerprint, or email address associated with your PGP key.
The output will be similar to the following:
$ gpg --keyid-format=0xshort --fingerprint example@example.com
pub   rsa2048/0x509E9413 2026-07-20 [SC]
      Key fingerprint = 1CCA 7D83 9880 E743 6BD7  8B92 9922 BEC6 509E 9413
uid           [ultimate] Example (Example key pair) <example@example.com>
sub   rsa2048/0x8E6447AD 2026-07-20 [E]
In this example, the PGP key ID is 0x509E9413.
The key ID uniquely identifies the key and should be used to confirm that the correct public key has been exchanged with Westpac.
To verify that the correct key has been uploaded, compare the Key ID displayed in iLink with the PGP key ID. The values should match.
Importing Westpac's PGP public key
Westpac will provide its PGP public key for import into your public keyring. This key is used to encrypt files destined for Westpac and to verify digital signatures created by Westpac.
Importing and trusting the key is a two-step process:
Import Westpac's public key into your keyring
$ gpg --import <westpac-public-key-file>Verify that the key was imported successfully:
$ gpg --list-keysThe output should include an entry for the imported Westpac public key.
The output will be similar to the following:
$ gpg --import 0x6F879EC7.asc
gpg: key B21F31756F879EC7: public key "Qvalent TEST2024 RSA AES SHA2 <securityinbox@qvalent.com>" imported
gpg: Total number processed: 1
gpg:               imported: 1

$ gpg --list-keys
[keyboxd]
---------
pub   rsa2048 2026-07-20 [SC]
      1CCA7D839880E7436BD78B929922BEC6509E9413
uid           [ultimate] Example (Example key pair) <example@example.com>
sub   rsa2048 2026-07-20 [E]

pub   rsa2048 2024-12-03 [SC]
      562E2C2488F8B0E1F5726FECB21F31756F879EC7
uid           [unknown] Qvalent TEST2024 RSA AES SHA2 <securityinbox@qvalent.com>
sub   rsa2048 2024-12-03 [E]
In this example, the key B21F31756F879EC7 has been successfully imported into the keyring. The imported key appears with a trust level of [unknown], which is expected until the key has been verified and trusted.
Sign Westpac's PGP public key with your PGP private key
$ gpg --sign-key <westpac-key-id>You may be prompted to enter the passphrase for your private key.
The output will be similar to the following:
$ gpg --sign-key B21F31756F879EC7

pub  rsa2048/B21F31756F879EC7
     created: 2024-12-03  expires: never       usage: SC
     trust: unknown       validity: unknown
sub  rsa2048/97CDDA090E8B2C8C
     created: 2024-12-03  expires: never       usage: E
[ unknown] (1). Qvalent TEST2024 RSA AES SHA2 <securityinbox@qvalent.com>


pub  rsa2048/B21F31756F879EC7
     created: 2024-12-03  expires: never       usage: SC
     trust: unknown       validity: unknown
 Primary key fingerprint: 562E 2C24 88F8 B0E1 F572  6FEC B21F 3175 6F87 9EC7

     Qvalent TEST2024 RSA AES SHA2 <securityinbox@qvalent.com>

Are you sure that you want to sign this key with your
key "Example (Example key pair) <example@example.com>" (9922BEC6509E9413)

Really sign? (y/N) y
To verify that the key has been signed successfully, list the keys in your keyring. Westpac's PGP public key should have a trust level of full:
$ gpg --list-keys
gpg: checking the trustdb
gpg: marginals needed: 3  completes needed: 1  trust model: pgp
gpg: depth: 0  valid:   1  signed:   1  trust: 0-, 0q, 0n, 0m, 0f, 1u
gpg: depth: 1  valid:   1  signed:   0  trust: 1-, 0q, 0n, 0m, 0f, 0u
[keyboxd]
---------
pub   rsa2048 2026-07-20 [SC]
      1CCA7D839880E7436BD78B929922BEC6509E9413
uid           [ultimate] Example (Example key pair) <example@example.com>
sub   rsa2048 2026-07-20 [E]

pub   rsa2048 2024-12-03 [SC]
      562E2C2488F8B0E1F5726FECB21F31756F879EC7
uid           [  full  ] Qvalent TEST2024 RSA AES SHA2 <securityinbox@qvalent.com>
sub   rsa2048 2024-12-03 [E]
Decrypting a file from Westpac
Files sent by Westpac are typically encrypted using your PGP public key and digitally signed using Westpac's PGP private key.
To decrypt and verify a file, you must have access to:
- Your PGP private key, which is used to decrypt the file.
- Westpac's PGP public key, which is used to verify Westpac's digital signature.
Decrypt and verify a file
$ gpg --output <decrypted-file> --decrypt <encrypted-file>Replace:
<decrypted-file>with the output file to create.<encrypted-file>with the encrypted file received from Westpac.
If the file was encrypted for your key, GnuPG will use your private key to decrypt it. If the file was digitally signed by Westpac and Westpac's public key has been imported into your keyring, GnuPG will also verify the signature during the decryption process.
Decrypt and verify a file in an automated environment
$ gpg --batch --pinentry-mode loopback --passphrase-file <passphrase-file> --output <decrypted-file> --decrypt <encrypted-file>Replace:
<passphrase-file>with a file containing the passphrase for your PGP private key.<decrypted-file>with the output file to create.<encrypted-file>with the encrypted file received from Westpac.
Protect the passphrase file appropriately, as it contains sensitive information.
Encrypting, signing and ASCII-armouring a file
Before sending a file to Westpac, it must be encrypted using Westpac's PGP public key and digitally signed using your PGP private key. GnuPG automatically compresses data before encryption unless configured otherwise.
Encrypt and sign a file
$ gpg --armor --recipient <westpac-key-id> --local-user <key-id> --output <encrypted-file> --encrypt --sign <original-file>Replace:
<westpac-key-id>with the key ID of Westpac's PGP public key.<key-id>with the key ID, fingerprint, or email address associated with your PGP key pair.<encrypted-file>with the output file name.<original-file>with the file to encrypt.
If your private key is protected by a passphrase, GnuPG will prompt you to enter it before creating the digital signature.
Encrypt and sign a file in an automated environment
$ gpg --batch --pinentry-mode loopback --passphrase-file <passphrase-file> --armor --recipient <westpac-key-id> --local-user <key-id> --output <encrypted-file> --encrypt --sign <original-file>Replace:
<passphrase-file>with a file containing the passphrase for your PGP private key.<westpac-key-id>with the key ID of Westpac's PGP public key.<key-id>with the key ID, fingerprint, or email address associated with your PGP key pair.<encrypted-file>with the output file name.<original-file>with the file to encrypt.
Protect the passphrase file appropriately, as it contains sensitive information.
Best practices
Concurrent connection limits
Westpac imposes limits on the number of concurrent SFTP connections that can be established by a customer. These limits vary by environment:
| Environment | Concurrent connection limit |
|---|---|
| Test | 3 |
| Production | 6 |
To operate within these limits, Westpac recommends the following best practices:
- Close SFTP connections as soon as file transfer operations have completed.
- Reuse existing connections where possible rather than establishing new connections for each file transfer.
- For Production environments, consider reserving a pool of up to three connections for uploads and three connections for downloads.
- Implement appropriate connection retry and back-off logic to avoid repeatedly attempting new connections when the connection limit has been reached.
Troubleshooting
SFTP troubleshooting
Unable to connect to SFTP host
Complete the steps in Testing basic connectivity (TCP) to confirm that a TCP connection can be established to Westpac's SFTP service on port 22.
If a TCP connection can be established but an SFTP session cannot, the issue is likely related to SSH authentication, SSH configuration, or access controls.
When troubleshooting SSH connectivity, run the client with verbose logging enabled and review the debug output:
$ sftp -vvv <username>@<host>The verbose output can help identify authentication failures, host key validation problems, protocol negotiation issues, and connectivity restrictions.
Common issues are described below.
kex_exchange_identification: Connection closed by remote host
This error typically indicates that a TCP connection was successfully established, but the remote server closed the connection before the SSH key exchange could be completed.
Common causes include:
- The source IP address has not been correctly allow-listed.
- The connection is originating from a different public IP address than the one provided during the iLink Connectivity Setup process.
- A firewall, proxy, or other network security device is interfering with the connection.
Confirm that the public source IP address configured in iLink matches the public IP address from which the connection is originating.
Unable to negotiate with 203.39.159.31 port 22: no matching host key type found. Their offer: rsa-sha2-512,rsa-sha2-256
Your SSH client does not support the host key algorithms offered by the server.
Modern SSH servers use the rsa-sha2-256 and rsa-sha2-512 host key signature algorithms, which are extensions of the legacy ssh-rsa algorithm that use SHA2 hashing instead of SHA1.
This error typically occurs when using an outdated SSH client that does not support RSA-SHA2 host key algorithms.
To resolve this issue, upgrade your SSH client to a current version that supports rsa-sha2-256 and rsa-sha2-512.
Prompted for a password when connecting
If you are prompted for a password when establishing an SFTP connection, the SSH public key presented by your client was not accepted by the server.
Confirm the following:
- The SSH private key specified by your SFTP client matches the SSH public key uploaded through the iLink Connectivity Setup process.
- The correct SFTP username is being used.
- The SSH public key has been uploaded to the correct environment (Test or Production).
- The SSH private key file is readable by the account running the SFTP client.
Review SFTP client verbose logging for Offering public key and Authentication succeeded messages to confirm that the expected key is being used.
Shell request failed when connecting
This error commonly occurs when an SSH client attempts to open an interactive shell session instead of establishing an SFTP session. Westpac's SFTP service provides SFTP access only, interactive SSH shell access is not permitted.
Always connect using an SFTP client such as OpenSSH sftp, WinSCP, or another SFTP-compatible application. If you attempt to connect using an SSH client (for example, ssh <username>@<host>), the connection will be rejected and you may receive a shell request failed or similar application-level error.
Unable to upload files
If you are unable to upload files to Westpac's SFTP service:
- Confirm that the local file exists and that your application is referencing the correct local file path.
- Confirm that the correct incoming directory has been configured in your application or SFTP client.
- Review your SFTP client logs for any permission or file transfer errors.
- Contact your Qvalent Implementation Consultant to verify the directory configuration and permissions associated with your SFTP user account.
Unable to download files
If you are unable to download files from Westpac's SFTP service:
- Confirm with your Qvalent Implementation Consultant that files are present in your outgoing directory.
- Confirm that the correct outgoing directory has been configured in your application or SFTP client.
- Confirm that the expected file name or file pattern matches the files available on the server.
- Confirm that the account running your application has permission to write to the destination directory on the local server.
- Review your SFTP client logs for any file transfer or permission errors.
Assistance with third-party SFTP solutions
Westpac and Qvalent can provide assistance with third-party SFTP software on a best-efforts basis; however, support is limited to general connectivity and integration guidance.
Examples of assistance that may be provided include:
- Reviewing your configuration to confirm that it performs the equivalent steps described in the Software installation section.
- Providing guidance on the required SFTP, SSH, and PGP configuration parameters.
- Assisting with the interpretation of connection logs and error messages.
- Requesting information from your software documentation to help identify potential configuration issues.
As Westpac and Qvalent do not provide support for third-party software products, we may be unable to diagnose product-specific issues.
If the issue cannot be resolved, we recommend contacting your SFTP software vendor or support provider for assistance.
PGP troubleshooting
WARNING: message was not integrity protected
When decrypting files, GnuPG may display the following warning:
gpg: WARNING: message was not integrity protectedThis warning can occur when processing files generated by systems that use older OpenPGP formats, including the version of SDS E-Business Server used by Westpac.
In these cases, the warning does not necessarily indicate that the file has been corrupted or tampered with. Instead, it indicates that the encrypted message did not include a Modification Detection Code (MDC), which is used by newer OpenPGP implementations to provide additional integrity protection.
The most important messages to review are the signature validation results. A Good signature message confirms that the file was successfully verified using Westpac's public key and that the signed content has not been modified since it was signed.
If signature verification fails, or if you receive a BAD signature message, do not process the file and contact your Qvalent Implementation Consultant for assistance.
Prompted to trust Westpac's PGP public key when encrypting
This warning indicates that GnuPG does not trust the public key sufficiently to verify the identity associated with it.
Before using the key, verify that its fingerprint matches the fingerprint provided by Westpac.
You can then assign an appropriate trust level:
$ gpg --edit-key <westpac-key-id>
gpg> trust
After assigning a trust level and saving the change, retry the encryption operation.
Note that trust levels are maintained locally within your GnuPG keyring. For most business partner keys, Full trust is typically appropriate once the fingerprint has been independently verified. Avoid assigning Ultimate trust to keys that are not your own.
Determining which PGP public keys a file was encrypted for
Use the following command:
$ gpg --list-packets <encrypted-file>The output identifies the key IDs and user IDs associated with the recipients that can decrypt the file.
When Westpac encrypts a file for a customer, it is typically encrypted for both:
- The customer's PGP public key
- Westpac's PGP public key
This allows either party to decrypt the file using their corresponding PGP private key.
This approach allows customers experiencing decryption issues to provide the encrypted file to Westpac for investigation, as Westpac can also decrypt the file using its own PGP private key.
Prompted to overwrite an existing output file when encrypting
You may receive a prompt similar to:
File 'XXX.asc' exists. Overwrite? (y/N)To allow GnuPG to overwrite existing output files without prompting, use the --yes parameter in your script. For automated environments, --yes is commonly used together with --batch to suppress interactive prompts.
Avoiding duplicate file processing when polling
A common approach is:
- Create a directory named
PROCESSINGon the SFTP server. - Move files from the
OUTGOINGdirectory into thePROCESSINGdirectory before processing them. - Process files from the
PROCESSINGdirectory. - Once processing has completed successfully, either delete the file or move it to a
PROCESSEDdirectory for audit and recovery purposes.
This approach reduces the risk of processing the same file multiple times and helps prevent files from being missed during subsequent polling cycles.